Find Internet products and info

Multiple indexes and AI combined

4Internet is a search engine built for people who work with or buy Internet-related products and services. We blend multiple indexes, proprietary ranking, and AI tools to return results focused on networking, hosting, domains, security, and related topics. The home page highlights popular tools, resources, and topical results to help you get started quickly. Part of the 4SEARCH network of topic specific search engines.

சத்தமில்லாமல் VI அறிமுகம் செய்த இரண்டு புதிய திட்டம் அதிக வேலிடிட்டி உடன் பல நன்மை

மூன்றாவது மிக பெரிய டெலிகாம் நிறுவனமான Vodafone Idea VI அதன் கஸ்டமர்களுக்கு இரண்டு புதிய ப்ரீபெய்ட் திட்டத்தை கஸ்டமர்களுக்கு கொண்டு வந்துள்ளது. இந்த திட்டத்தின் விலை ரூ,599 மற்றும் ரூ,899 ஆகும், இந்த இரு திட்டங்களிலும் அன்லிமிடெட் காலிங், டேட்டா மற்றும் அதிக நாகல் வேலிடிட்டி என பல நன்மை வழங்குகிறது. இதில் ரூ,599 திட்டத்தில் 56 நாட்கள் வெலிடிட்டியும் மற்றும் Rs 899 திட்டத்தில் மொத்தம் 84 நாட்கள் வேலிடிட்டியும் வழங்குகிறது, மேலும் இந்த […] சத்தமில்லாமல் VI அறிமுகம் செய்த இரண்டு புதிய திட்டம் அதிக வேலிடிட்டி உடன் பல நன்மை VI அதன் கஸ்டமர்களுக்கு இரண்டு புதிய ப்ரீபெய்ட் திட்டத்தை கஸ்டமர்களுக்கு கொண்டு வந்துள்ளது. இந்த திட்டத்தின் விலை ரூ,599 மற்றும் ரூ,899 ஆகும் இந்த திட்டத்தின் நன்மைகள் மற்றும் பல விவரங்களை தெளிவாக பார்க்கலாம் வாங்க. மூன்றாவது மிக பெரிய டெலிகாம் நிறுவனமான Vodafone Idea VI அதன் கஸ்டமர்களுக்கு இரண்டு புதிய ப்ரீபெய்ட் திட்டத்தை கஸ்டமர்களுக்கு கொண்டு வந்துள்ளது. இந்த…
631 words
More in Internet & Telecom

Ringleader of Indian Fake Robbery/Immigration Scam Gets Just Two Years in Jail

A man living in Chicago who was convicted of running an immigration fraud ring has been handed a two-year prison sentence for arranging hundreds of fake armed robberies so migrants can use the police reports to gain legal visas. Parth Nayi, 29, was charged with organizing the fake robberies from 2022 to 2024 at small restaurants, convenience stores, and gas stations across Chicago and the suburbs, prosecutors said, according to CWBChicago. Nayi, though, recruited illegal migrants, “with most being of Latin and South American origin,” to pretend to be robbery victims so they could file for the visa protection, according to the report. The migrants would pay Nayi upwards to $10,000 to be part of the scheme. The scheme was usually carefully orchestrated with the assistance of store employees and the fake robbery was staged so that no one was ever really injured. But one such fake robbery…
319 words2 outlets
More in Ransomware

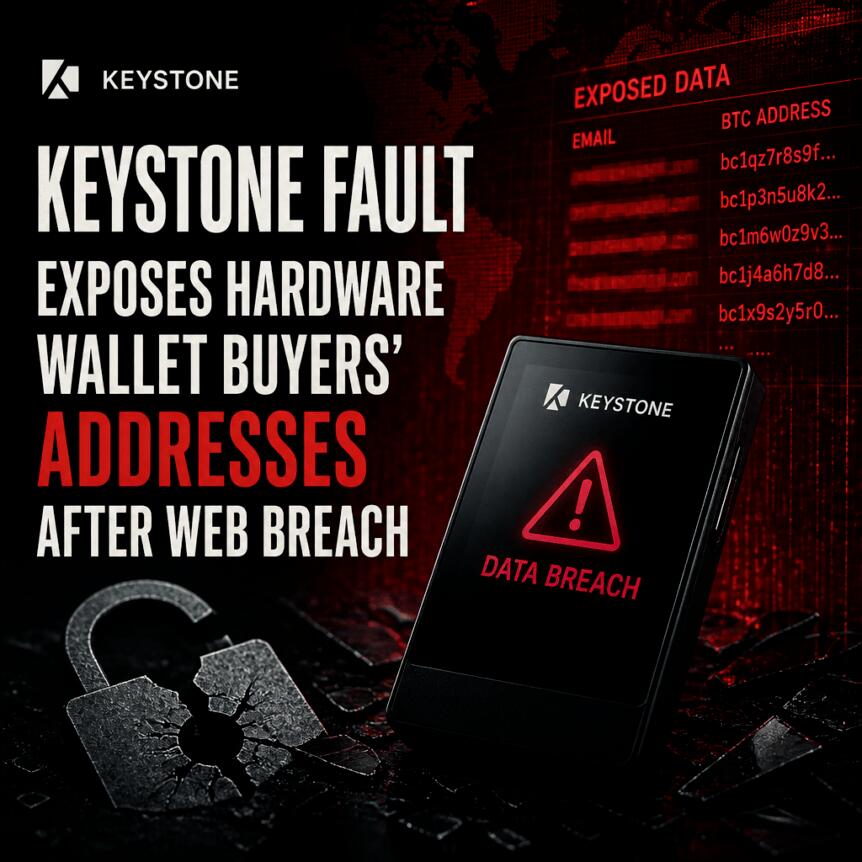
Keystone Fault Exposes Hardware Wallet Buyers’ Addresses After Web Breach

Keystone, the crypto hardware wallet company, has disclosed that a website security breach exposed customer shipping and order details to an unauthorized third party. The incident, which Keystone says was identified earlier in the week and confirmed after reviewing API activity with Shopify, could increase the risk of targeted phishing and other scams. The disclosure comes amid rising concern for real-world “wrench attacks,” a category of crimes where victims are threatened or harmed to force them to surrender cryptocurrency. Security firm CertiK reported that it recorded 52 verified wrench attacks worldwide in the first half of 2026—up from 39 during the same period in 2025. Keystone stated that it detected suspicious activity earlier in the week and confirmed the breach on Friday after reviewing API activity with Shopify. In the company’s description, an unauthorized third party…

465 words2 outlets
More in Data Breaches

Building a Pre-Ship Supply Chain Security Filter for PHP, npm, and PyPI

The filter catches four attack classes that dominated Black October: The filter is a single Go binary (fast, no runtime dependencies) invoked as a CI step. It reads lockfiles, queries threat intel in parallel, applies policy, and exits non-zero on violations. Each ecosystem has a parser implementing a common interface. Each provider implements a common interface for parallel querying. Add structured logging to the engine: Ship logs to your observability stack (Datadog, Grafana Loki, etc.) and alert on critical > 0. A: Those tools run after dependencies are installed and only check known CVEs. This filter runs before install, catches typosquatting/dependency confusion (which have no CVE), analyzes install scripts for malicious behavior, and enforces a unified policy across all three ecosystems in a single CI step. A: Yes. FindLockfiles walks the entire repo root. Each lockfile is parsed…

793 words
More in Malware and Phishing